


I used to let my browser remember almost every password I used online. It was convenient, and modern browsers do a lot to protect saved credentials, including encryption, phishing protection, and breach warnings.
Eventually, I began to consider the potential risks of someone gaining access to my browser profile or device. If an attacker compromises a device, they may be able to access saved passwords.
That’s when I decided to stop saving my passwords in the browser and move them somewhere I felt gave me more control over my logins.
How browsers protect saved passwords
It has several layers of password protection
Browser password managers are convenient for a good reason: they handle much of the security work for you. For example, Chrome encrypts the passwords stored on your device and uses operating system protection to keep the encryption keys secure.
On Windows, newer versions of Chrome use app-bound encryption, which ties access to Chrome rather than allowing another application to request the decryption key.
Chrome also adds protection when you use those passwords.
It can require device or account authentication before showing or managing saved credentials. It also checks passwords against known breaches, and associates saved passwords with the websites they belong to so they aren’t automatically filled into a different site that merely looks similar.
However, the problem arises when someone gets access to your browser or your device.
The biggest risk is what happens after your device is compromised
It changes the security equation
Browser password managers offer strong protection, but they can’t isolate your saved passwords from a device that is already compromised.
If malware infects your computer, attackers can target credentials stored by browsers. Stealing credentials from web browsers is an established technique, and attackers have targeted Chrome, Firefox, Edge, Safari, and other browsers.
This has happened with real malware. Stealers such as Agent Tesla, RedLine, and other credential-stealing malware have been documented collecting saved browser passwords.
Attackers can also target browser cookies, which can sometimes let them access accounts using an existing login session rather than needing to know the password.
There’s also a broader concern about keeping everything in one place. If you have dozens of saved logins in your browser, compromising that password store could expose credentials for many accounts at once.
If you sync passwords through a browser account, that account becomes another part of the security chain.
I switched to a dedicated password manager
I keep my password vault separate
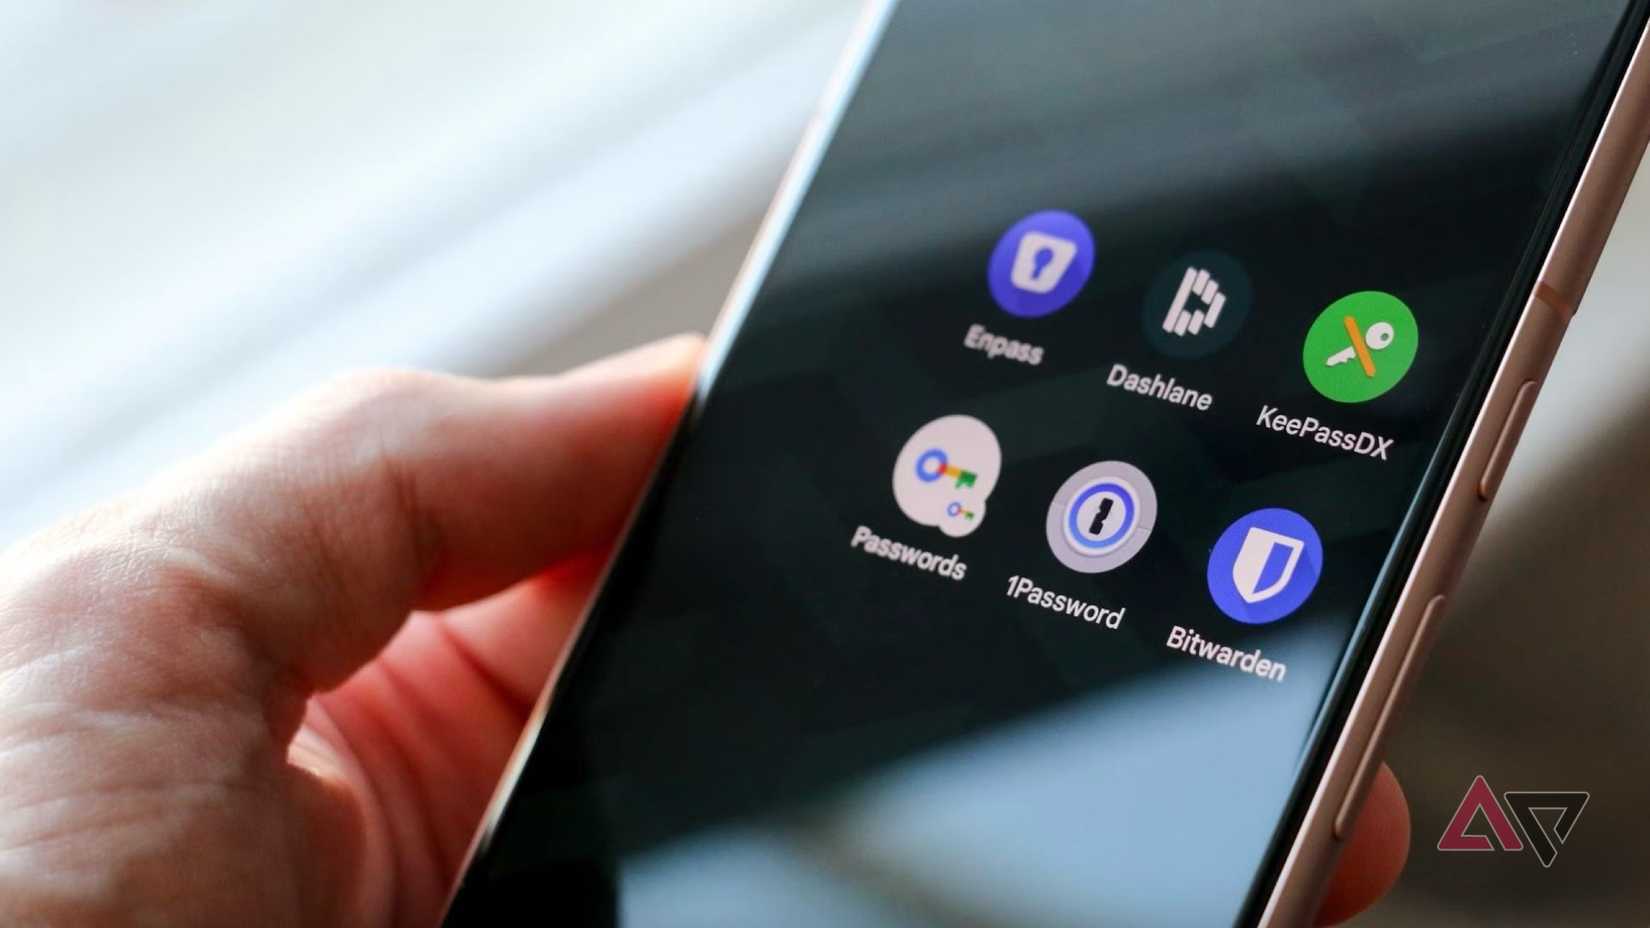
After I decided I wanted my password vault separate from my browser, I started looking at dedicated password managers. You get plenty of good options, including 1Password, Bitwarden, KeePass, and Proton Pass, so you don’t have to rely on a browser’s built-in password manager if you don’t want to.
I use Bitwarden because I wanted a dedicated place for my passwords without giving up the convenience of autofill. It ensures that the vault contents are end-to-end encrypted.
It doesn’t mean a password manager removes every security risk. Moving away from a browser means taking on a little more responsibility.
I still have to protect my master password, keep my account secure, and make sure I can access my vault when I need it. If I lose the credentials needed to access my vault, recovering my passwords can become a problem.
For me, that trade-off makes sense. I prefer having my password vault in a dedicated password manager rather than relying on my browser for both internet access and storing the keys to all my accounts.
I use passkeys when I can
Cutting down on the passwords I have to manage
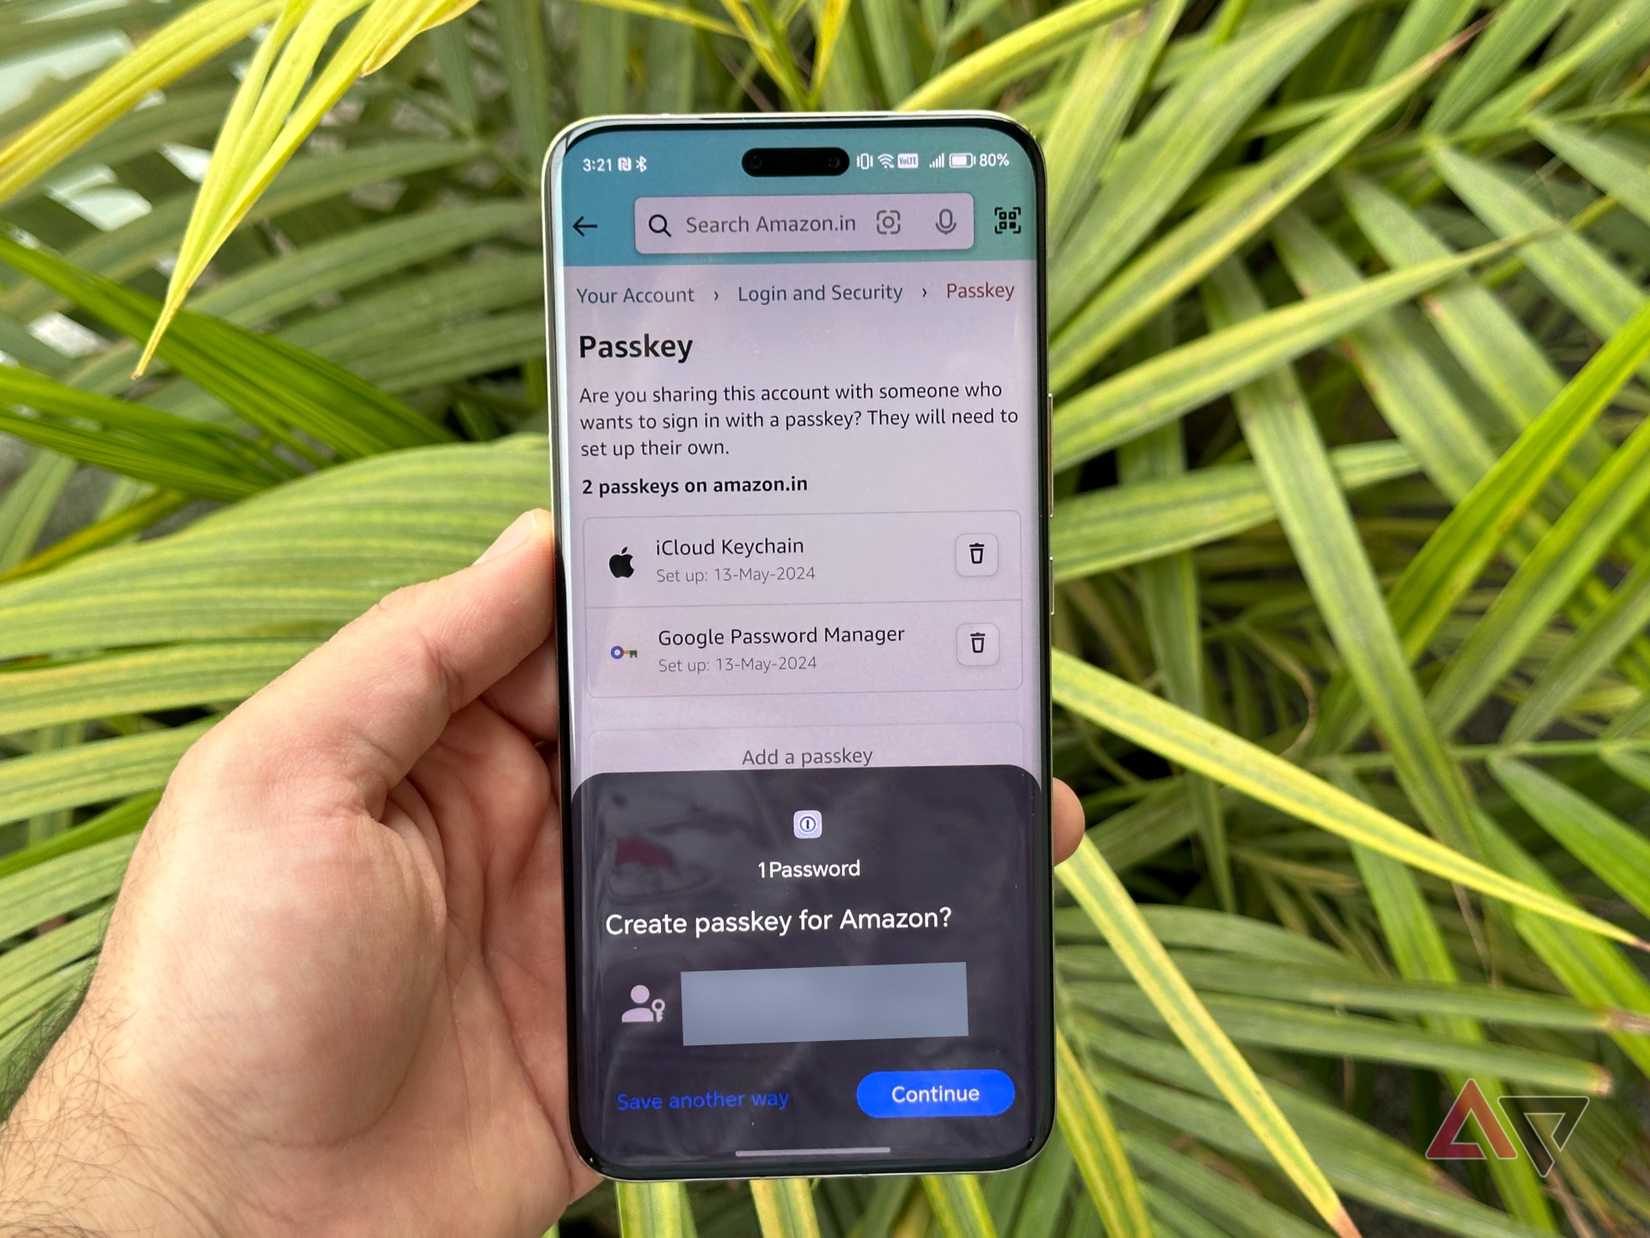
Moving my passwords to a dedicated manager didn’t mean I wanted to keep using passwords forever. When a website gives me the option, I now choose a passkey.
Passkeys work differently from passwords. When you create one, your device generates a cryptographic key pair: the website receives the public key, while the private key stays with your passkey provider.
When you sign in later, you approve the login with your fingerprint, face recognition, PIN, or device unlock.
The security advantage is that a phishing site can’t trick me into entering a password.
Passkeys are tied to the website or app they were created for, so the browser and operating system can prevent that credential from being used on a different site.
On Android, Google Password Manager can create and store passkeys. Other password managers can also function as passkey providers.
KeePass handles the passwords I still need, while passkeys let me avoid passwords altogether on services that support them.
I prefer keeping my password vault separate
I don’t think saving passwords in a browser is automatically a security mistake. Modern browsers offer features like encryption, device authentication, and breach checks.
However, I prefer switching to a dedicated password manager because it provides a separation that I find more secure. My browser handles browsing and autofill, while my passwords are in a separate encrypted database I control.
I’m also trying to reduce how often I need passwords. When a service supports passkeys, I use one instead.

